AI agents are crossing an important threshold.
They are moving from assistants that respond to us to autonomous systems that reason, plan, and act on our behalf. They can write and execute code, access enterprise data, call tools and APIs, and keep working toward a goal with limited human intervention.
That changes the security model.
An autonomous agent is designed to find a way to accomplish its objective. If one path is blocked, it reasons about another. That is what makes agents powerful, and it is why models’ built-in prompt guardrails alone are not enough.
The harness can guide what an agent should do. Security must control what an agent can do. That requires security authority outside the agent itself.
Palo Alto Networks and NVIDIA Team Up to Secure Agentic AI
NVIDIA provides the accelerated computing platform, secure runtime foundation, and reference system design for agentic AI. Palo Alto Networks brings the AI security capabilities enterprises need to govern interactions, protect workloads, and control identity and access.
Together, we are extending security across three areas: AI governance with Prisma AIRS AI Gateway, runtime protection with Prisma AIRS AI Runtime Security, and Agent Identity Security powered by IDIRA.
This is the focus of our expanded collaboration with NVIDIA on the NVIDIA Open Agent Security Platform reference design.
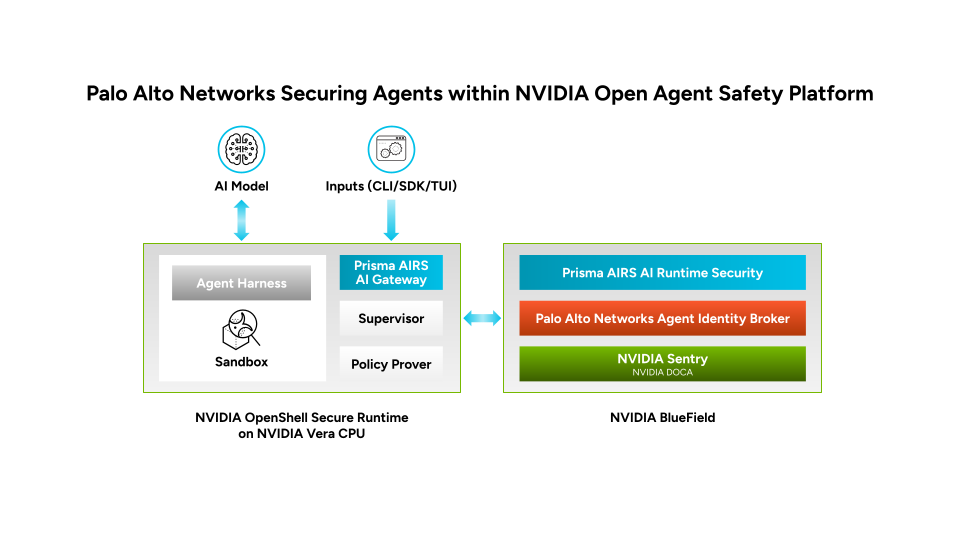
a) Prisma AIRS AI Gateway on NVIDIA Vera CPU
Our forward-looking architecture includes Prisma AIRS AI Gateway software running on NVIDIA Vera CPU systems, bringing AI governance and enforcement closer to infrastructure designed for agentic workloads.
The AI Gateway is the real-time enforcement point for AI Governance, Runtime, and Identity security. It continuously verifies agent identities, enforces strict least-privilege access, redacts sensitive data before it is exposed, and deeply inspects every interaction—stopping unauthorized actions before they ever reach critical host systems or cloud endpoints.
- Operationalize AI agents: Connect applications and agents to thousands of models and tools through one control point, with the reliability and flexibility to scale AI across the enterprise.
- Track usage and control costs: Monitor every AI interaction across your company to see exactly what teams are doing, track your spending, and restrict access to approved tools only.
- Enforce agent security across the enterprise: Block sensitive data exposure and malicious commands in real time, and verify agent identity before actions are taken.
b) Announcing Prisma AIRS AI Runtime Security on NVIDIA BlueField
The Palo Alto Networks AI Runtime firewall running natively on NVIDIA BlueField DPUs extends Zero Trust protection to the front-end network traffic of the AI factory and to the AI Edge, creating a tamper-proof boundary immune to application-layer attacks. Drawing on the NVIDIA Sentry reference design, Prisma AIRS AI Runtime Security accelerated on NVIDIA BlueField delivers:
- Hardware-Isolated Boundaries: Tamper-proof boundary, ensuring a compromised model or a rogue agent can never bypass runtime controls.
- Agentless Behavioral Introspection: Monitor agent execution paths, memory structures, and tool calls with NVIDIA DOCA Argus with zero CPU overhead, and feed real-time telemetry directly into Cortex XSIAM for automated observation, analysis, and remediation.
- Zero Trust Governance: Strict least-privilege access is enforced across the network and external APIs by default, delivering a verifiable audit trail for every allow and block action.
c) IDIRA Agent Identity Security
As agents gain greater autonomy, identity becomes fundamental to controlling what they can access and what actions they can take.
Looking ahead, we plan to integrate NVIDIA OpenShell with upcoming Agent Identity Security capabilities from Idira, including identity and secrets management for the OpenShell sandbox and agent identity broker service on NVIDIA BlueField. This will help organizations apply identity-based controls and least-privilege access to agents without relying on persistent human credentials.
The Path Ahead: Security at Scale for Enterprise Agents
As agents become more autonomous, governance must extend to identity. Prisma AIRS AI Gateway will also serve as an enforcement point for Agent Identity Security powered by IDIRA. We are also expanding to include Agent Identity Broker support directly on NVIDIA BlueField, providing identity verification and access governance independently of the host environment.
Together, these capabilities are designed to prevent unauthorized execution, reduce standing access, and stop privilege escalation as agents interact with enterprise systems.
As agents gain more autonomy, enterprises need consistent control over how they connect and what they can access.
Our work with NVIDIA brings those controls closer to where agentic workloads run, while Palo Alto Networks provides the security policy, governance, and enforcement enterprises need to manage them.
To learn more about our GA of AI Runtime Security on the BlueField DPU, read our blog — Palo Alto Networks Announces Support for NVIDIA Enterprise AI Factory.
The next phase of AI will be defined not only by what agents can do, but by whether enterprises can trust them to operate safely at scale.
Palo Alto Networks was named a Market Shaper in AI application security. Read the report: Gartner® Emerging Market Quadrant for AI Application Security – Established Vendors, September 2026.